
The password manager your team will actually use.



Everything your employees need to log in securely

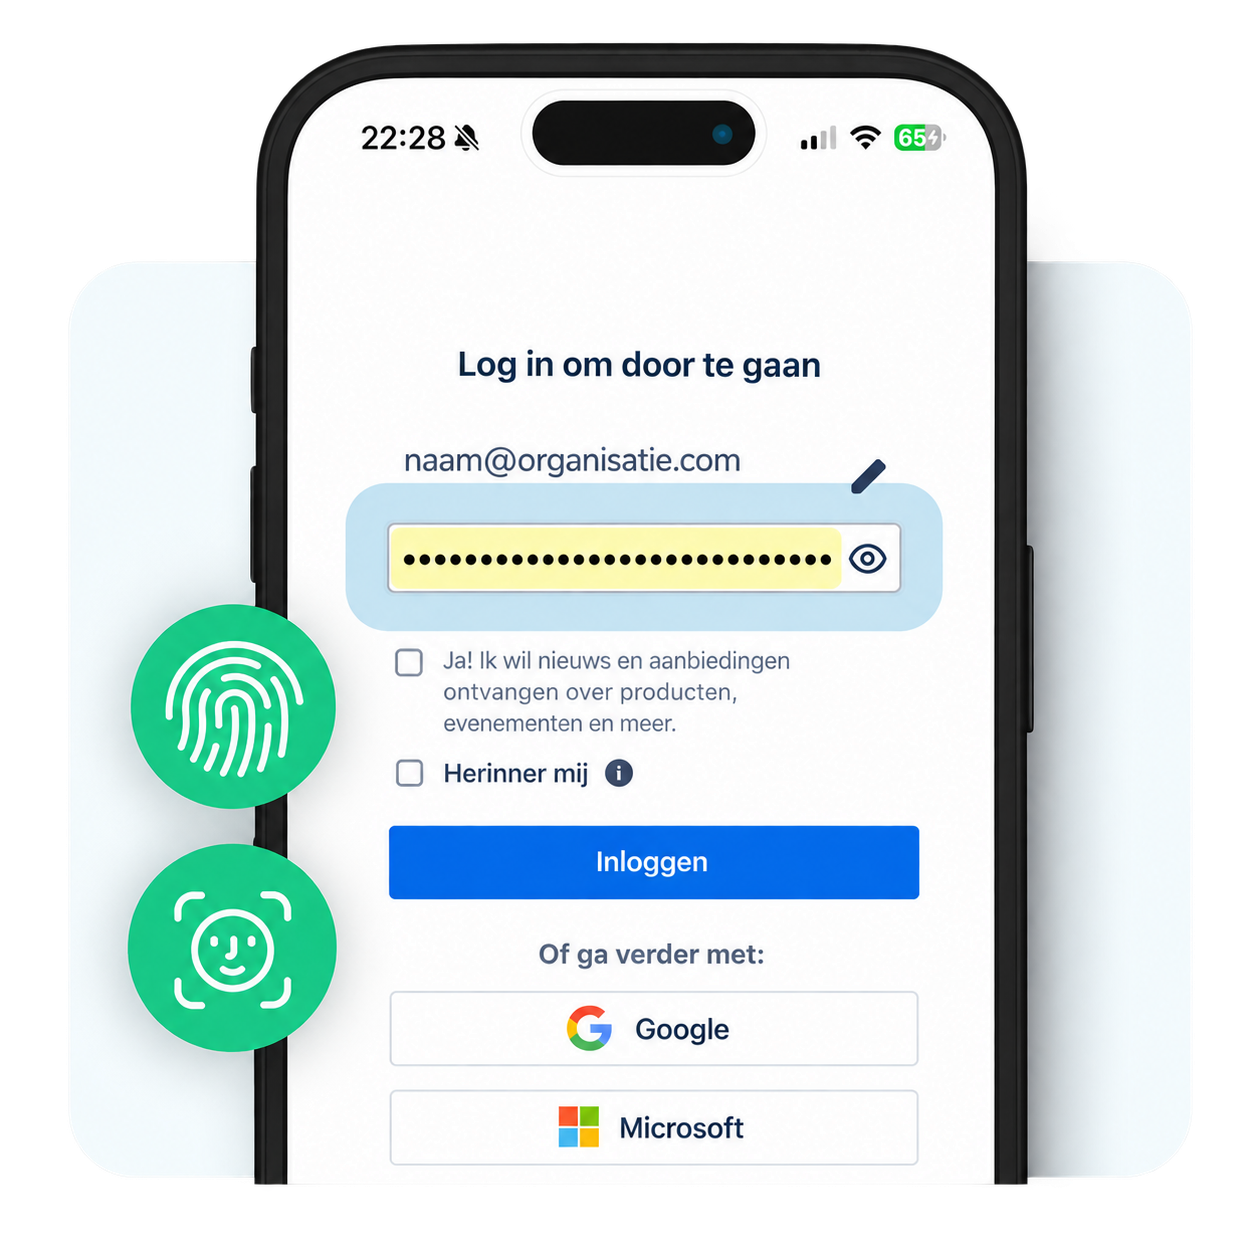
Phishing-proof login

Share access securely

Manage secrets securely

Linked to work account

Free for personal use
See it for yourself









A password manager only works if everyone uses it.
01
Fast, centralised deployment
02
Tailored
training
03
Insight into adoption
04
Making it a habit at home, too

What isn't stored cannot be leaked.


Traditional password managers primarily help users manage passwords securely and often fill them in automatically. In doing so, they solve part of the password problem.
MindYourPass goes further. In addition to a powerful password manager, it provides organizations with continuous insight into applications, authentication methods, password usage, and login risks. Based on this, organizations can centrally apply and enforce security policies, ensuring that secure login is not dependent on the behavior of individual users.
Furthermore, MindYourPass supports both passwords and passkeys from a single platform. Organizations gain insight into their passwordless readiness and can realize the transition to passkeys step-by-step, while applications that still rely on passwords remain securely supported.
MindYourPass also distinguishes itself through its patented vaultless technology, which ensures that passwords are not stored in a traditional password vault.
This is how MindYourPass helps organizations continuously improve digital access: from secure and phishing-resistant password usage today to a controlled transition to passwordless.
MindYourPass was developed for organizations that want to manage digital access in a secure, controllable, and future-proof way. The platform is suitable for small, medium, and large organizations alike and is used across sectors including government, healthcare, education, housing associations, accounting, and the corporate world.
Whether an organization wants to get started with secure password management, implement passkeys, comply with laws and regulations like NIS2, or gain better insight into applications and login risks: MindYourPass supports every stage of the journey toward secure digital access.
Thanks to its modular design, organizations can start by gaining insight through monitoring and then expand the platform with secure password management, passkeys, and centralized security policies.
MindYourPass's patented vaultless technology calculates a password every time it is needed. As a result, passwords never need to be stored in a central or local password vault.
For every site or web application, the exact same password is calculated based on a set of unique data. Because the same input always leads to the same result, the password can be regenerated on any authorized device without ever needing to be stored.
Furthermore, the calculation is domain-specific. This ensures that a unique password is automatically used for every web application, preventing a password from being used on another website or phishing domain.
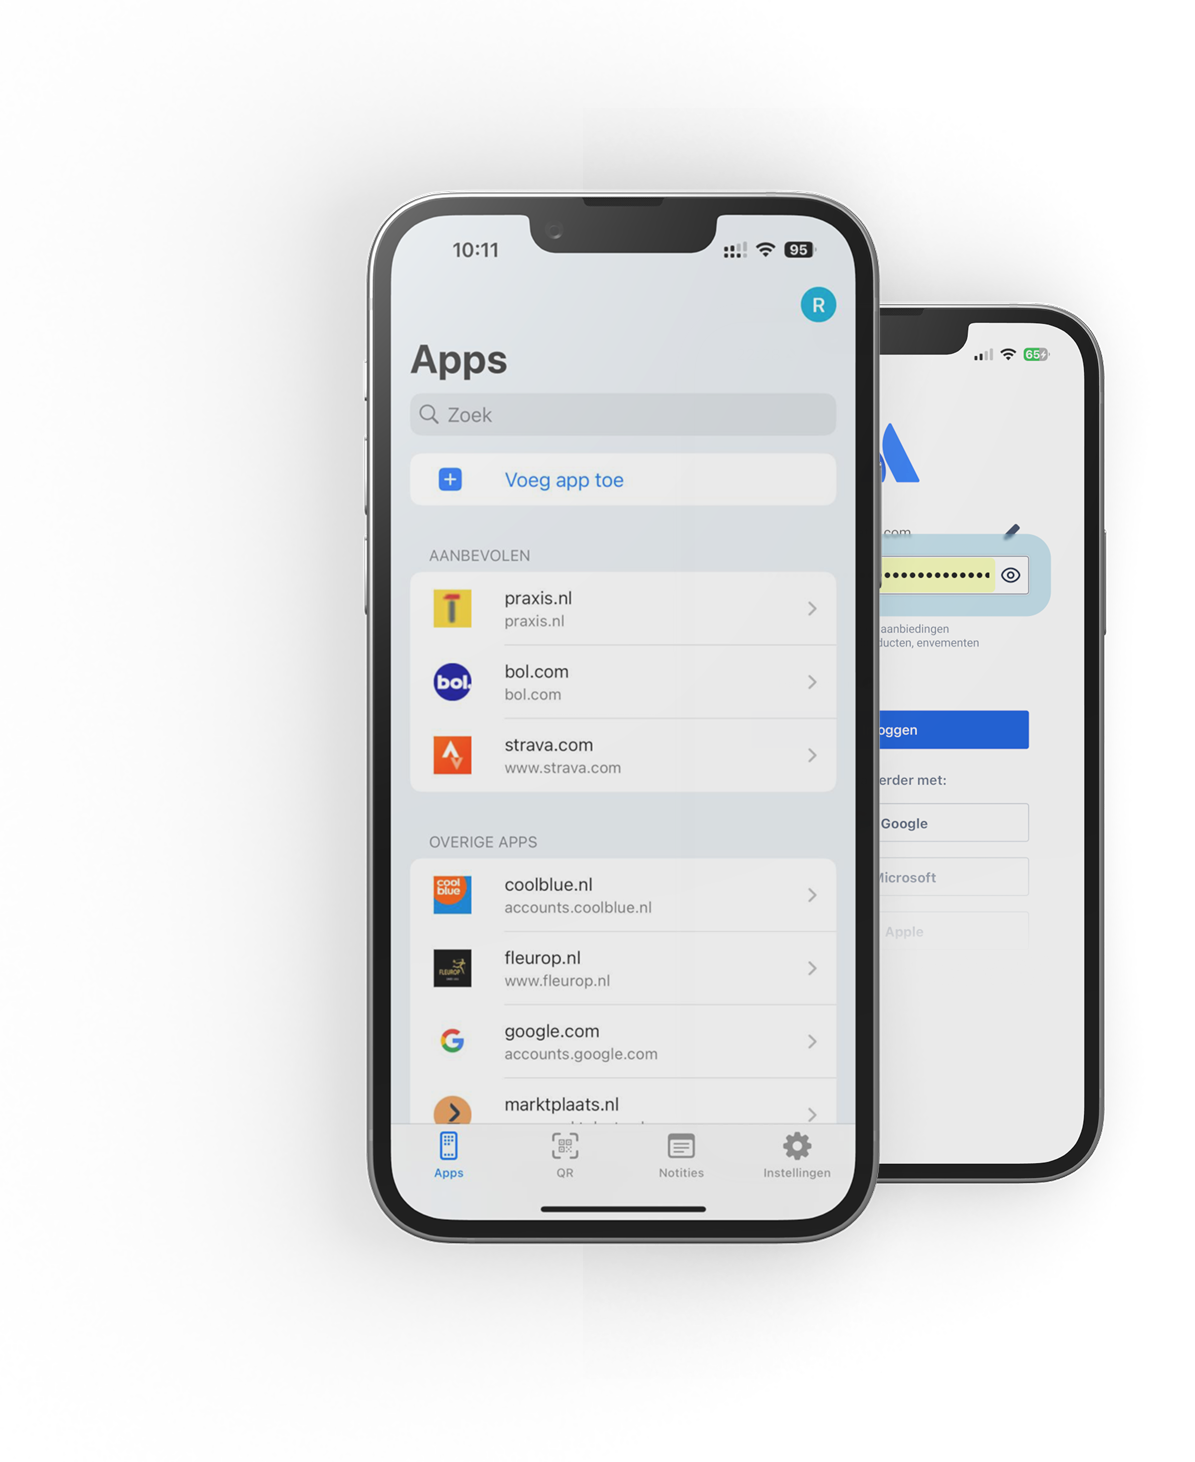
For the user, this works just like a traditional password manager: after verification, the correct login credentials are automatically filled in. Behind the scenes, however, passwords are calculated rather than stored.
MindYourPass helps organizations significantly reduce phishing risks during login.
When users log in with a passkey, authentication is inherently phishing-resistant.
For web applications that still use passwords, MindYourPass provides an additional layer of protection. Its patented vaultless technology generates a unique, domain-bound password for every website. This ensures that passwords cannot be interchanged between sites, meaning a password intended for one website cannot be used on another.
In addition, the MindYourPass Password Manager only auto-fills login credentials on the correct website. This eliminates the need for users to manually enter or copy and paste passwords, further reducing the risk of successful phishing.
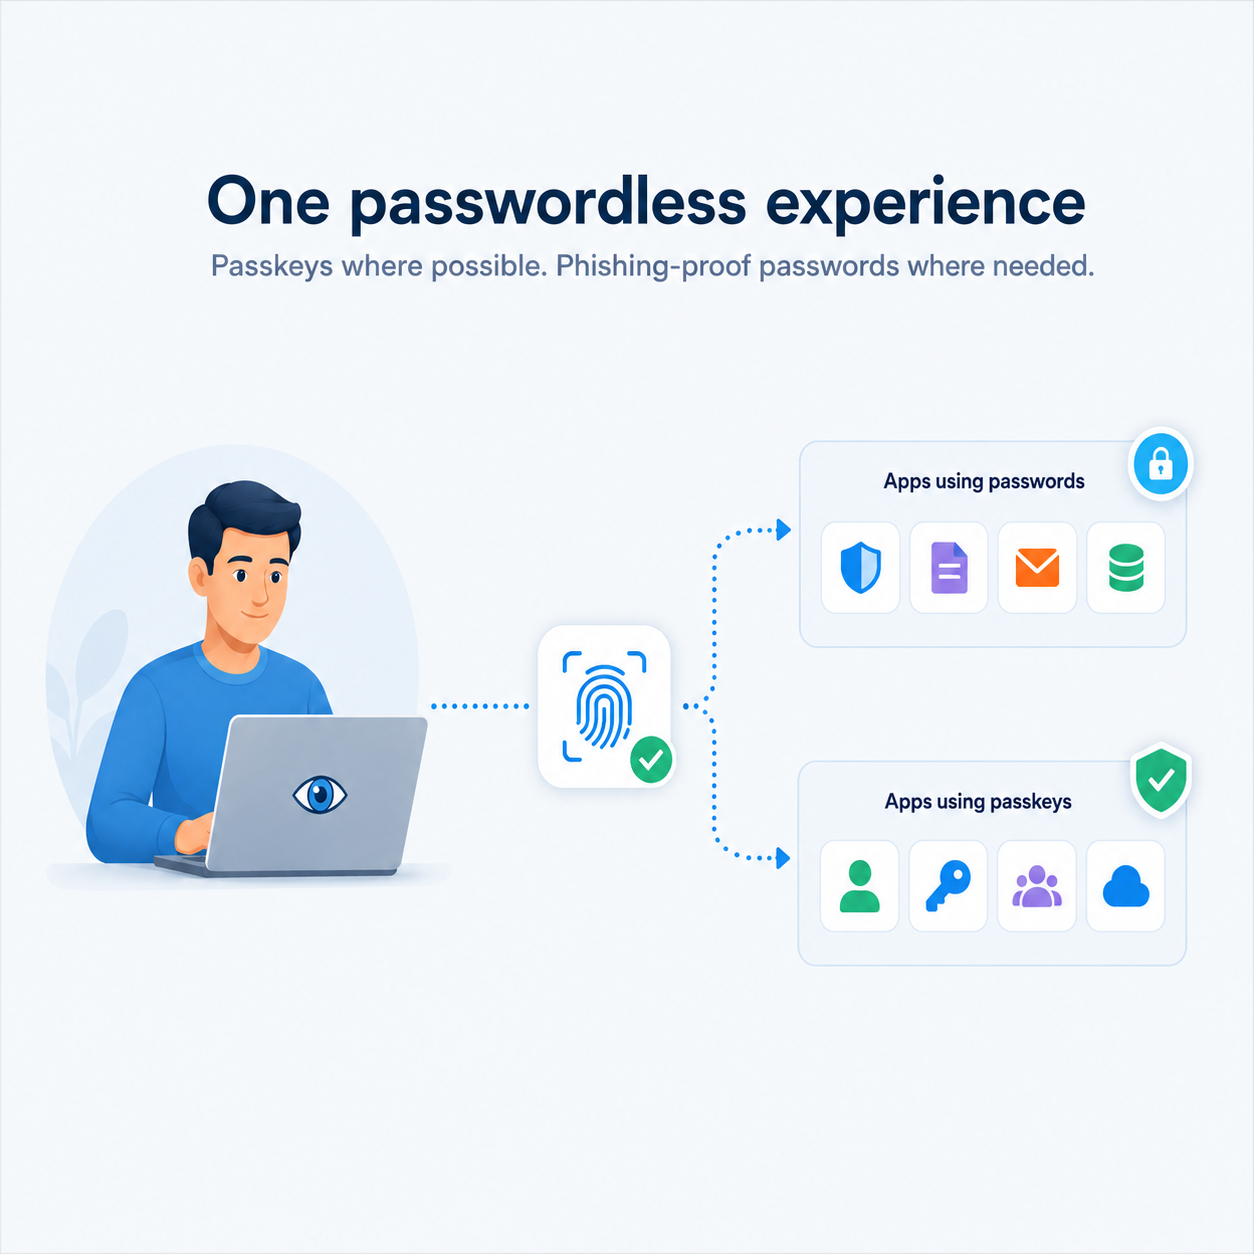
In this way, MindYourPass offers a single, secure login experience for both password-based and passwordless applications.
The implementation of MindYourPass always begins with a technical setup.
For a MindYourPass Assessment or Monitoring, the implementation consists of the technical installation of the MindYourPass Agent.
Implementing the MindYourPass Password Manager involves both a technical software setup and an organizational rollout. In addition to the technical configuration, this includes a focus on user deployment, communication, onboarding, training, and user adoption.
Separate implementation guides are available for each solution, describing the implementation steps in detail.
Yes. MindYourPass integrates with existing Single Sign-On (SSO) solutions, such as Microsoft Entra ID, Okta, and other Identity Providers that support SAML or OpenID Connect.
Web applications that already support SSO continue to use the existing Identity Provider directly. MindYourPass does not take over this authentication and does not change the existing SSO login flow.
Users sign in to MindYourPass using SSO via the organization's Identity Provider. From there, they can also securely log in to web applications that are not linked to SSO and still require a password. For the user, this feels like the same simple login experience as SSO, for example using Windows Hello, biometric verification, or a FIDO2 security key, without them ever having to enter passwords again.
This creates a single, consistent login experience for all web applications, regardless of whether they use SSO, passkeys, or passwords. MindYourPass calls this Total Sign-On: extending the benefits of Single Sign-On to web applications that do not yet support SSO.
This offers similar benefits for organizations as well. Access to the MindYourPass Password Manager can be managed centrally via the Identity Provider. As a result, existing security measures, such as user provisioning, deprovisioning, and conditional access, can also be applied to access for web applications that still rely on passwords.